Categories
Privacy & Consent

CCPA Compliance – How To Prepare Your Mobile App For New Privacy Laws

As of the 1st January 2020, the California consumer privacy act (CCPA) will introduce new rights for every citizen living in the state of California.

These changes will affect the way companies look at privacy. The legislation is currently only applicable to consumers in the state of California. However, as we will discuss, the act will likely have an impact across the US.

Along with the GDPR, which offers consumers similar data and privacy rights in the EU, the CCPA is something that all businesses need to consider. This starts with a brand’s databases, CMP, and website, but it also includes any mobile app.

Apps will be subject to the same scrutiny, and under the regulation, developers will need to find a solution to comply with the legislation fully.


What is the CCPA

First, let’s look at the technical side of the new legislation.

The act allows any consumer-based in California access to all information or data that a company has related to them.

The act also states that this information should include a full list of the third-parties that the data is shared with.

It also allows consumers to request that companies delete this data or stop them from sharing it with one or all of the relevant third-parties.

As well as this, the CCPA also means that companies will have to do more to explain to consumers what types of data they are collecting, why they are doing it, and how consumers can opt-out.


What does CCPA cover?

The act seems to take a broader approach than GDPR in terms of what constitutes personal information:

  • Any personal identifier such as name, alias, address, unique or online personal identifier, IP address, email, account name, social security number, passport, or driving license number.
  • Commercial data that includes records of property, product or services, or other historical purchase data.
  • Geolocation data
  • Biometric data
  • Professional information or employee data, such as employee time tracking, or employee engagement. You can even use a timeclock calculator to gather this data. 
  • Internet or other electronic network activity information including, but not limited to, browsing history, search history and information regarding a consumer’s interaction with a website, application or advertisement


What happens if my mobile app is not compliant?

According to the CCPA, companies will have 30 days to comply with the when regulators notify them of a violation. After this, is there is no resolution, the regulator will issue a fine of up to $7,500 for each record.

Despite this initial fine, companies are under threat from another area that is covered in the act. The bill allows an individual to sue a company. This occurs if a consumer gives written notice to a company that they have had their privacy rights violated. If the company cannot find a resolution, then the consumer can bring a class-action suit against the company.


How to become compliant

For mobile apps, it can be more challenging to become compliant with privacy laws. Many tools for manage consumer privacy preferences are web first, and there aren’t a lot of tools that exist for developers to manage consent and comply with the regulation.

Under CCPA, apps will need to understand the data that they have on all of their users. This needs to be attached to a single consumer to provide information about the data that the company has on an individual. This means a centralized location is needed that can access this information.

As well as this, how the data is used will need to be communicated to the user, including third-party uses.

Lastly, consumers need to be able to access this, manage their choices, and request that this information be deleted.

So, many dedicated nodeJS developers need an interface that clearly explains which data is being collected and why. It will also need to allow users to opt-out and define which third-parties can access this data.

Sound complicated? Well, luckily, there is a solution.


Tamoco’s mobile-first CMP

A CMP is a powerful tool that should be implemented anywhere where consumer data is being processed or stored. For these reasons, it makes sense to have a CMP that can cope with large amounts of consumer preferences and can manage these in several different locations and platforms.

The Tamoco CMP collects user preferences in applications. It allows consumers to collect and manage use preference for data collection and data use.

Our CMP is the world’s first mobile CMP that allows developers to comply with data privacy legislation such as the GDPR and the CCPA.

With a straightforward integration app developers can take control of their app and deliver privacy management at scale for all of their users.


What is the CCPA?

The act allows any consumer-based in California access to all information or data that a company has related to them. The act also states that this information should include a full list of the third-parties that the data is shared with. It also allows consumers to request that companies delete this data or stop them from sharing it with one or all of the relevant third-parties. As well as this, the CCPA also means that companies will have to do more to explain to consumers what types of data they are collecting, why they are doing it, and how consumers can opt-out.

Related: read more about how Tamoco sources consented location data.

Categories
Privacy & Consent

What Is A Consent Management Platform? All You Need To Know 2026

Introduction

Since the introduction of more detailed privacy regulations, such as the GDPR and the CCPA, businesses have started to take consumer consent and data privacy seriously.

Consumer data comes in multiple forms, and it’s used for many different purposes, from advertising personalization to monetization.

Because of this, collecting and managing consumer preferences on how all of their data is used across these different use cases is not exactly the simplest of tasks.

Privacy laws have meant that businesses need a robust solution that provides consumers with this choice. Enter the consent management platform (CPM) – a toolkit that is designed to do just this.


What is a CMP

For consumer-facing publishers, there is a huge issue here. These businesses work with multiple partners across the advertising ecosystem. Each partner has numerous uses for consumer data, from advertising to personalization. Asking and managing this consent across an entire user base is a daunting task.

This is where a consent management platform comes in. By collecting user preferences for different data types and different uses and various partners, CMPs provide this functionality.

Think of a CMP of something that sits between the publisher and the user. It informs users about the type of data that the publisher will collect, whether through forms, or another method, and what this data will be used for. It allows consumers to modify these settings, stores this, and gives consumers a chance to opt-out and change these settings.

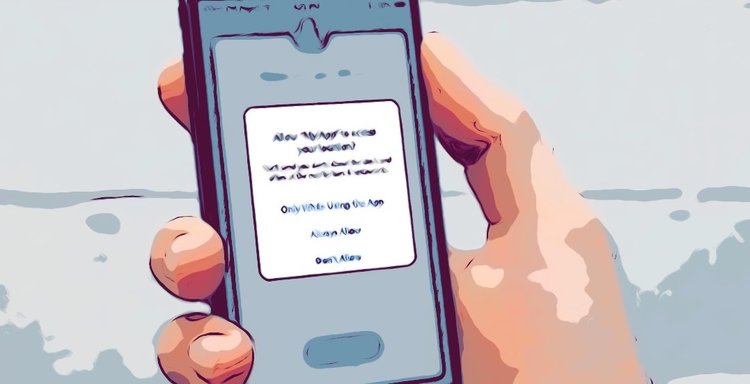
What this looks like for the consumer is usually a simple dialogue. This dialogue allows them to choose how their data is used. These preferences are stored and ultimately control of how user data moves between the publisher and the broader advertising ecosystem.

As a lot of new privacy regulations require businesses to offer this level of functionality to consumers, consent management software is a vital tool for any modern company.


Why do you need a CPM?

To give users the option to take control of their data.

CPMs provide the consumer with the opportunity to control their data and how it is used. They allow consumers to understand who is using their data and for what for.

CPMs give consumers the ability to revoke this access and update these preferences at any time. The tools then automatically communicate these consumer requests throughout the data supply chain.

This proves detailed control of personal data at an end-user level. This level of functionality puts the user in control and increases trust between a publisher, app, or other consumer-facing platform and the users that ultimately bring them revenue.


To comply with privacy regulation

The main reason that you need a CMP is to comply with relevant privacy laws and regulations. These tools are useful because they can be universally integrated across every consumer-facing platform, allowing companies to comply instantly.

Regardless of whether you’re an EU based business or not, correctly managing user preferences should be a priority. For website owners and publishers, offering users the choice and allowing them to achieve these at any point is fundamental to how regulators see the data-driven world.


To deliver better experiences, improve personalization or monetize user data

First-party data uses still require the same level of opt-in as data that is sent on to third-party solutions.

That means if you are using customer or user data for analytics or insights, you’ll need to implement the choice controls that come with a CPM.

This also applies for personalization, whether first-party page personalization or passing data onto third-parties to deliver personalized ads on your inventory.

As well as this, CPM functionality is required for data monetization or other activities where a user’s personal data is used for monetization purposes.


Are all consent management platforms compliant with GDPR and CCPA?

Well, no. You’ll have to check with the current privacy laws to be 100% sure. An excellent way to understand which CPMs are is to check to see if they use the IAB framework.


IAB transparency and consent framework

The IAB GDPR transparency and consent framework was built to understand what is needed from a CPM from a technical standpoint to comply with the GDPR. If that sounds like a mouthful of acronyms, then don’t worry, it can be a little confusing.

What this does in practice is sets several hoops for CMPs to jump through for their consent management platforms to be GDPR compliant. So, look out for this term when choosing a CPM as it means they have taken the time to verify that they are following best practices according to the leading industry body.

At the time of writing, there is currently no equivalent for the CCPA.


The Tamoco consent platform + SDK

A CMP is a powerful tool that should be implemented anywhere where consumer data is being processed or stored. For these reasons, it makes sense to have a CMP that can cope with large amounts of consumer preferences and can manage these in several different locations and platforms.

The Tamoco CMP collects user preferences in applications. It allows consumers to collect and manage use preference for data collection and data use.

Our CMP is the world’s first mobile-first CMP that allows developers to comply with data privacy legislation such as the GDPR and the CCPA.

With a straightforward integration app developers can take control of their app and deliver privacy management at scale for all of their users.

Related: read more about how Tamoco sources consented location data.
Categories
Privacy & Consent

Advertising Cookies & Retargeting – What’s Changed + Solutions

It seems that you can’t go anywhere in the world of online advertising at the moment without the conversation moving onto the role of advertising cookies, and what the future holds.

With the implementation of GDPR last year, the California Consumer Privacy Act coming into play in 2020, the cookie has come under increasing pressure.

Combine this with Apple’s Intelligent Tracking Prevention and the whispers that Google is also looking to block third-party cookies, and you can understand why everyone in the space is a little worried about what the future holds for the cookie.

We’re going to look at this future, how the cookie works, and how marketers and advertisers can adjust for any upcoming changes in how the advertising industry uses web cookies.


What are advertising cookies? How do cookies work for advertising?

First of all, what role do cookies play in the world of advertising?

Well, cookies are small code snippets that store information related to how the user behaves on the web. This cookie is stored on the user’s web browser and can be used accessed to store and change data related to the user.

Cookies can store a wide range of information, such as the pages you have visited and for how long.

We can divide these further types:

First-party cookies

First-party cookies are created by the publisher or website owner when a visitor is on their site. Cookies enable website visitor tracking which helps a business understand which user is returning and ensure that the page content is right for that user. Often, this is something like language or another element that helps with the user experience.

These cookies also include analytics, such as Google Analytics, which used cookies to measure how users use the site.

Third-party cookies

Third-party cookies are used in the digital advertising ecosystem for retargeting and for behavioral-based targeting. Adding these types of cookies to pages allows advertisers to understand how users behave across the web. Using these, they can build a profile that can be selected to target with ads that are more personalized to each user.


What are cookies used for?

Advertising cookies can be used for analytics and for managing the user experience. But we are interested in the role that they have in the advertising ecosystem.

Here cookies are used mainly to retarget users based on which site and which pages they have visited. What started as a simple way to deliver products to users who had already seen them has now developed into sophisticated methods to target users that have previously visited a specific page or product.

The other side of the advertising cookie is to build audiences based on profiles. As a user visits a site, this information is used to build a profile for that user. This profile contains information such as age, gender, and interests. These profiles allow marketers to build and create new audiences that are relevant for their product or proposition.


What’s changing

The most significant change to the advertising industry in the last few years has been the drive for transparency and user privacy.

Privacy regulators have introduced legislation that limits how advertising cookies can be used to collect user data. These have created a massive issue for the advertising ecosystem, which relies heavily on third-party cookies to build profiles and target audiences based on behavior.

This is because programmatic advertising relies on these third-party cookies as the basis for user-level targeting and attribution. Without this process, marketers can’t target users with more personalized ads and understand when these ads lead to conversions.

As well as this, the people who bring the internet to users have also started to take a tough stance on the issue. At the time of writing, Apple has already announced an anti-tracking update to its native browsers, which blocks the use of third-party cookies. Firefox has implemented a similar policy, and there are reports that Google, who’s browser user base makes up over 60% of web usage, is looking at a similar process.

Another implication for advertisers is that the world has become more mobile-first since the invention of the web cookie. Users are using apps and mobile solutions much more instead of sitting behind a computer.

With all this, it makes a little more sense that advertisers are worried about how these changes will impact their business. But it’s not all doom and gloom – we have some examples of how advertisers can still deliver personalized ads and retargeting campaigns that work.


Potential solutions

Focus on people and context

Instead of looking at the type of consumer and using this to build audiences, advertisers can focus on context.

Rather than focus on the user, placing greater emphasis on where the user is can be an effective way to target audiences. For example, using keywords to gauge purchase intent. Or using a user’s real-world location or environmental factors to understand factors beyond the user that make them ideal for targeted advertising.


Focus on first-party data and reliable first-party providers

First-party data will become an even more valuable currency for targeting users. Solutions that can combine first-party insights and compliance with privacy regulations will be invaluable for advertisers.

These datasets can help to target consumers reliably and with consent from the end-user. For example, anonymized first-party mobile location can be used to retarget users that have visited a physical store.


Wait for a persistent identifier

A persistent identifier is a solution that is commonly suggested as the ecosystem moves away from the cookie. Using this form of identifier, that sits with the consumer and requires explicit compliance with privacy regulations could be a solution.

The problem here is getting this to exist in one form, that’s standardized and that everyone can agree upon. Some areas of the advertising supply chain have introduced this already – but these don’t follow the same standards, making it difficult for advertisers.


Look at other channels

Advertisers will begin to look at channels that don’t require third-party advertising cookies. These will include traditional channels such as email, TV, and app-based ads.

These systems allow advertisers to use a persistent identifier for personalized advertising and marketing.


Conclusion

Marketers and advertisers will need to think about how they can focus on people based personalization in a world where the advertising cookie no longer exists. First-party data or reliable first-party data providers will become a vital source of behavioral data. Using alternative behavioral information, such as location, is a great way to deliver retargeting and personalization at scale.

Mobile ad IDs are currently universal and tracking identity across the moble infrastructure is much simple than the web. The role of advertising cookies is changing and quickly. People-based advertising and first-party data could well be the solution that the industry is looking for.

Related: read more about how Tamoco sources consented location data.

Categories
Privacy & Consent

How to Meet GDPR Compliance for Geolocation Tracking?

Geolocation tracking has become a ubiquitous feature in modern applications and services. 

It allows companies to gather customers’ location-based data to improve user experience and offer more personalized services. 

However, with the implementation of the General Data Protection Regulation (GDPR) in the European Union (EU), companies that collect, process, use, or share geolocation data must ensure they comply with the strict data protection standards set by the regulation. 

So, if your company collects customers’ geolocation data to provide location-based services (i.e. weather, delivery, navigation, etc.) or build their behavioral profiles, modeling, and predictive analysis, it is essential to comply with GDPR.

In this article, we will explore what GDPR compliance exactly is, and how to meet its regulations for geolocation tracking.

What is GDPR Compliance?

The General Data Protection Regulation (GDPR) is a comprehensive data privacy regulation that was implemented in the European Union (EU) in May 2018. 

For the uninitiated, the regulation aims to protect the privacy rights of EU citizens & residents by setting strict standards for the collection, processing, and storage of personal data.

Companies that collect the personal data of their EU customers must follow the requirements set out in the GDPR. 

These requirements include:

  • Obtaining explicit consent from individuals to collect and use their data
  • Providing transparent information about the purpose and use of the data
  • Implementing appropriate measures to safeguard the data

Neglecting to comply with GDPR can result in hefty fines and reputational damage.

Currently, the GDPR fines are categorized into two tiers. 

Less serious breaches or violations can result in €10 million or 2% of the company’s annual revenue in fines, depending on which amount is higher.

Severe data breaches or violations can cost fines up to €20 million or 4% of the company’s annual revenue, whichever is higher.

How Does GDPR Affect Geolocation Tracking?

The GDPR has a significant impact on geolocation tracking as it classifies geolocation data as personal data. 

For the uninitiated, geolocation tracking refers to the collection and processing of location data from an individual’s device or other sources, such as GPS or Wi-Fi signals.

Companies then make sense of the collected geolocation data through data science and gain meaningful insights to make better decisions in real-time.

However, any company that now collects such geolocation data is subject to the GDPR’s strict data protection standards. 

So, if your company currently collects or processes the geolocation data of your EU customers, you must ensure that they are in compliance with the GDPR’s requirements.

How to Comply with GDPR for Geolocation Tracking?

Here are some steps companies can take to meet GDPR compliance for geolocation tracking.

1 – Evaluate What Your Company Already Does to Protect Geolocation Data

The first step in meeting GDPR compliance for geolocation tracking is to assess the current state of your company’s data protection practices. 

To do so, start by reviewing the procedures and systems in place for collecting, processing, and storing geolocation data. 

After that, determine if you have appropriate technical and organizational measures in place to protect the data, such as data encryption and access controls. 

Finally, identify any gaps in your current processes that need to be addressed to meet GDPR compliance.

2 – Create a Workflow to Obtain Explicit Consent Before Collecting Geolocation Data

Obtaining explicit consent is a crucial requirement of GDPR compliance for geolocation tracking. 

Companies must obtain explicit consent from individuals before collecting and using their geolocation data. 

Furthermore, the consent must be specific, informed, and customers must have the right to withdraw their consent at any time.

To ensure that consent is obtained in a compliant manner, create a workflow that obtains consent before collecting the data. 

3 – Add Provisions to Your Company’s Privacy Policy for Geolocation Tracking Data

Another requirement of GDPR compliance for geolocation tracking is transparency. 

Companies must provide clear and concise information about the purpose and use of geolocation data. 

To meet this requirement, you need to update your company’s privacy policy to include provisions related to geolocation tracking data. 

Furthermore, the policy must also inform individuals of the type of data collected, how it will be used, who will have access to it, and how long it will be retained.

4 – Educate Your Employees on How to Manage Collected Geolocation Data Properly

In addition to adding required GDPR related provisions, you must also educate your employees the appropriate ways to manage collected geolocation data and implications of not doing so.

Ideally, your employees should be able to comprehend what your company uses geolocation data for, and the potential risks to your customers involved. 

This means training your employees on how to obtain explicit consent, how to process and store the data securely, and how to respond to requests from individuals to exercise their data protection rights. 

Remember, this is an extremely important step towards complying with GDPR. After all, your employees are ultimately responsible for managing geolocation data that your company collects. 

So, organize regular training and refresher courses for your employees (and rest of the staff) to ensure that they are up-to-date on GDPR compliance requirements for geolocation tracking.

5 – Ensure Third Parties Your Company Shares Geolocation Data With are Also GDPR Compliant

If your company happens to share customers’ geolocation data with third parties, such as analytics providers or advertising partners, it’s crucial to ensure that those parties are also GDPR compliant. 

Before sharing geolocation data with any third party, make sure that your third-party providers also obtain explicit consent from your customers before processing their personal data and are completely transparent about it. 

Alternatively, you can also consider making this entire process automated by investing in a robust CAASM solution.

What is CAASM? — It’s a comprehensive cybersecurity solution that helps to take inventory of all cyber assets in your network, monitor attack surface, identify & remediate potential threats, and ensure compliance of your third-party vendors with relevant regulations (i.e. GDPR).

CAASM does this by making sure that your third-party vendors have implemented appropriate data protection measures in accordance with GDPR regulations. 

Additionally, CAASM also helps your company implement appropriate security controls and monitoring mechanisms to ensure that third-party vendors are complying with GDPR requirements. 

This usually includes regular security audits, assessments, contractual obligations for data protection, and ongoing monitoring of vendor activities.

Ending Note

The collection of geolocation data can provide organizations with access to highly personal information about individuals, making it a valuable commodity. 

However, such data collection practices can also raise concerns about privacy and potentially lead to noncompliance issues for businesses. 

That’s why meeting GDPR compliance for geolocation tracking is not just important but essential for any company that collects and uses location data. 

It not only ensures that the organization is in compliance with the law but also helps to build trust with customers by demonstrating a commitment to protecting their personal information.

By following these simple steps, not only you can easily achieve GDPR compliance but also demonstrate a commitment to ethical data practices that respect the privacy and dignity of their users.

Related: read more about how Tamoco sources consented location data.

Categories
Privacy & Consent

Android Developers Can Use Google AdMob And Comply With GDPR

Google is asking app developers who publish apps on its play store to obtain consent for data use and for ad personalisation through its AdMob platform. 

Due to the coming GDPR legislation which comes into effect on the 25th of May. Any business based in the EU will need to gain opt-in consent to collect or use any of their user’s personal data. 

This news places the responsibility of obtaining consent for Google’s services that are running in the background (such as AdMob targeting) on the shoulders of the publishers. Android developers are expecting to see some kind of software kit to help them obtain and manage this consent. As of now, and up until the new legislation kicks in, Google has not announced any SDK or toolkit that could solve this headache for Android developers. 

Many developers lacking the time or manpower to create such a kit are weighing up their options ahead of the legislation. Some have even hinted at switching of these third-party services for users int eh EU. 


The problem

Breaches of the legislation carry with it the threat of huge fines. User consent has always been an issue for app publishers. Creating a solution for obtaining consent and then managing this consent is no easy feat. Integrating this consent with third-party integrations (such as advertising solutions) adds another layer of complexity. 

For Android developers, the problem is a little more pressing as AdMob revenue is what keeps them afloat. Developers may find themselves stuck between a rock and hard place – turning off AdMob would instantly create a big hole in their revenue. However, keeping it on and exposing themselves to potentially destructive fines doesn’t seem like a viable option either. 


So what’s the solution?

With the right toolkit developers wouldn’t have to change their business model too much. Letting users opt out of ads might lose some revenue but it’s a necessary step to take to comply with the changing mood around privacy and transparency. 

Controlling user data in a responsible way makes sense because it builds trust and in the long term it will be beneficial for developers. 

Luckily for developers, there’s a toolkit that is addressing this problem. Via a dedicated SDK app, publishers can continue to use third-party ad integrations, such as AdMob. The toolkit obtains and manages user consent to help developers comply with regulations such as GDPR.

As well as this the toolkit will sync user consent across devices. All consent preferences are stored in a secure audit trail so that developers can call on consent history of their users. The audit trail also contains information on consent preferences that have been replayed to third parties. In the AdMob example when a user opts out of personalised ads in their app the consent SDK will relay this to Google. The audit will register this along with a timestamp and other relevant details.

The SDK provides this functionality for first-party app features as well as third-party integrations. It’s a comprehensive toolkit to take control of your user consent. 

This toolkit doesn’t need to only apply for Admb or even android. A wider conversation about the role of consent in mobile applications needs to be had. Developers should look at how consent is obtained, managed and communicated to third parties. 

Complying with GDPR is a shortsighted approach. Developers need to put their users first and think about how they can put these users back in control of their data.

[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”50px” bottom_margin=”20px”]

Get free early access to the consent toolkit 

We’ll get you set up for free as soon as it’s launched. 

[mkdf_button size=”” type=”” text=”Get started” custom_class=”” icon_pack=”font_awesome” fa_icon=”” link=”/contact-app” target=”_self” color=”” hover_color=”” background_color=”” hover_background_color=”” border_color=”” hover_border_color=”” font_size=”” font_weight=”” margin=””]
 
[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”20px” bottom_margin=”0px”]
 

Related: read more about how Tamoco sources consented location data.

Categories
Privacy & Consent

App GDPR Toolkit – How Developers Can Prepare Apps for GDPR

When GDPR is concerned, developers can’t afford to overlook app user privacy, consent and opt-in preferences. Here’s five tips that will get you compliant.

It’s a huge problem for app publishers. How can you comply with intimidating privacy legislation and maximise the number of users that are opted into your app services?

By some estimates over 50% of current apps are not compliant with the new GDPR legislation.

That’s because apps have multiple third parties and SDKs integrated. Many of these are asking for data on users.

It’s difficult for publishers to keep track of this. But it’s now the law to be in control of this data.

It shouldn’t have to be this difficult to comply with privacy regulation. And it shouldn’t be hard for your users to opt-in and out of individual preferences.

Lucky we think we’ve found a solution for developers to manage, sync and audit consent in their suite of mobile apps. 


Asking for consent and getting your users to opt-in

Complying with privacy legislation isn’t the most straightforward process.

And how do you make sure that you don’t spook your users into opting out of all services? User opt-in is important to obtain as it can be a great tool in which to drive engagement and retention, not to mention monetization.

You need to ask user to opt-in at the right time. And you need to be clear that they are in control. We tried to solve this problem by designing our consent toolkit to help developers obtain and manage user consent.

Many apps get opt-in timing wrong. Don’t ask for all permissions the first time that the user opens the app. Explaining the value that users will get in return for opting in for certain permission will mean that the user is better educated about what their data is being used for.

Make sure that your opt-in process is clear and be upfront with your users.


Manage user opt-out requests respectfully

Under new legislation is just as important to ensure that users can opt out as it is to obtain consent properly in the first place. To do this publishers must have a system in place that can allow their users to opt out of some or all of the permissions that they have previously opted in for.

This was one of the fundamentals that shaped the way our consent module works. We wanted our toolkit to make it as easy for users to opt-out and it is to opt-in. This needs to be done in a way that doesn’t just put the user in control of their data but allows them to choose which kinds of data is used by publishers.


Make sure you can manage consent across devices

Consent and user opt-in management are difficult enough to get right as it is. But this can be made nigh on impossible when you consider the fact that app users are constantly deleting apps and changing devices. 

Syncing user settings are important because if a user has revoked a permission on one device then to continue to use this could be a breach of privacy regulation. Also, if a user requests that all their data be deleted, this is difficult to do unless you can identify everywhere that the user has given access to data.

That’s one of the problems that the consent toolkit was built to solve. By using a series of unique identifiers it’s possible for developers using the toolkit to sync consent preferences. In this way, the consent toolkit manages a users consent and opt-in/opt-out preferences whenever they interact with an app or service.

This is especially useful when a user requests their data be deleted (or in GDPR terms – right to be forgotten). Having a toolkit that syncs across devices allows publishers to remove this data and stop collecting it wherever the user is seen in the future.

Sometimes it’s a messy infrastructure. What happens if a user updates consent preferences in one app, but uses other apps from you? Make sure you can sync this preference across your real-estate.


Integrate user consent with third parties

Apps rarely run in isolation. You might have third party services, or other SDKs that have access to our user’s data.

These need to be kept in sync with the user’s opt-in preferences. If your user says no to communication, this needs to be updated with third-party advertisers for example.

At Tamoco, our consent module allows apps to instantly update third parties with new user preferences. If a user asks for all of their historical data to be deleted this information needs to be relayed to third parties.

The consent SDK communicates this to third parties automatically when a user’s preferences are updated.

Information of this is then secured in a secure audit trail. The consent module will automatically ask third parties to confirm that they have received these requests for changes in a users preferences. When this is (or is not) received this is saved in the audit trail, along with timestamps and relevant information.

This means that developers can ensure that their users’ opt-in preferences are respected in third-party integrations. It’s important to be able to follow an audit trail to prove that this information was relayed to third-party partners and integrations such as SDKs.


Make sure you have a secure audit trail

With the correct procedure in place, developers don’t need to worry about manually managing consent. But what happens if you ever need to prove that your app has protected user data.

App developers need a way of storing the history of user consent. It should be easy for developers to prove that historical consent has been obtained.

In our consent toolkit we provide developers with an audit trail to do just this. Everytime a user changes their consent preferences then the SDK automatically records this with time stamp.

This ensures that app publishers are always covered. This information is easily viewed and provided for reference. Third-party consent is also stored in the audit trail. All requests for opt-out are sent to third parties and the record of this is then stored in the audit.

[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”50px” bottom_margin=”20px”]

The consent toolkit is launching soon, sign up below to get free early access

[mkdf_button size=”” type=”” text=”Get early access” custom_class=”” icon_pack=”font_awesome” fa_icon=”” link=”/contact-app” target=”_self” color=”” hover_color=”” background_color=”” hover_background_color=”” border_color=”” hover_border_color=”” font_size=”” font_weight=”” margin=””]
 
[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”20px” bottom_margin=”0px”]

Related: read more about how Tamoco sources consented location data.

Categories
Privacy & Consent

GDPR & CCPA For Apps – Tips For Privacy Compliant Apps

Let’s look at GDPR, the CCPA and how you can make sure that your app is ready for the coming changes.

What’s the most important currency around? It’s data. It’s used to fuel everything from your personal virtual assistant to your social media feed. But let me tell you one thing about this data. It’s private, it needs to be safeguarded and soon, fellow app developers, it will be the law for you to ensure this.

Data is so omnipotent in our digital lives. Privacy regulation is set to make data handlers liable for how they collect, protect, store and remove this data. Some have predicted that up to 55% of apps aren’t ready for this change.

But you thought GDPR is only for email marketers. Wrong. Complying with privacy regulations is integral to running a successful mobile app business. As a mobile developer, under the new legislation, you will be responsible for all the personal data from your app.

That’s right – as of the 1st Jan 2020 responsibility will rest with you to ensure that you are in control of user data. But it doesn’t have to be all doom and gloom. The GDPR and CCPA are an opportunity for developers to create effective relationships with their users. It also means that you can offer up a great app experience at the same time.


But what is GDPR and CCPA?

GDPR stands for the General Data Protection Regulation and it came into effect on the 25th of May 2018. It is designed to protect data as it is collected and stored. It is also in place to ensure that the user is in control of their data. It seeks to allows the user to easily opt-out and remove their data when they so desire.

The CCPA is similar and will come into play on the 1st of Jan 2020 – the California Consumer Privacy Act is a bill meant to enhance privacy rights and consumer protection for residents of California, United States.

For apps, this means that a proper system for opt-in, data collection and data storage will need to be in place. As well as this the infrastructure to opt-out and be forgotten are essential to comply with the legislation.

There are some key principles to define when looking at the legislation from a developer’s perspective. We will help to explain these next and look at exactly what these principles mean for developers, as well as practical advice for app owners.

[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”50px” bottom_margin=”20px”]

The consent toolkit is launching soon, sign up below to get free early access

[mkdf_button size=”” type=”” text=”Get early access” custom_class=”” icon_pack=”font_awesome” fa_icon=”” link=”products-sdk-consent/” target=”_self” color=”” hover_color=”” background_color=”” hover_background_color=”” border_color=”” hover_border_color=”” font_size=”” font_weight=”” margin=””]
 
[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”20px” bottom_margin=”0px”]


Explicit consent

This is a key requirement for mobile apps. The legislation says that businesses must request and receive consent to collect use and move personal data. Further, this request must be made and given in clear intelligible and easily accessible way. It cannot be confusing. As well as this the user must be able to withdraw consent as quickly as they can give it.

This means that apps will need to communicate better with their users. They must clearly define the type of personal data they collect around users. Developers will need to explain why this data is collected and obtain clear consent to collect this information.

Practically this means that you may wish to ask for certain types of personal data at different points of the user experience. For example, it’s generally a better idea to ask users for data consent at a point where it is relevant to the action that the user is performing.

So don’t ask for every permission under the sun the first time your app is opened. It might be better to wait for the right moment to communicate these to the user.

This also gives you a better opportunity to communicate the value that the user will receive by opting-in for this type of data collection. It also means that you can clearly explain opt-out procedures as well (but more on that later).

For example, we help our partner apps to obtain consent for location permissions by providing a dialogue with the user at the right moment. This could be when the user is looking for nearby venues or searching for local deals.

By clearly explaining to the user at this moment it allows the user to come to an informed decision on how they want to share their personal data with the app. This complies with the ‘explicit consent’ as defined in the GDPR legislation.

Find out more about asking for consent by speaking to our app team.


The right to be forgotten

One of the keys focuses of the legislation is the right to be forgotten. This means that app developers will need to create a system of opting-out that allows users to be in control of the data collected through the app.

As previously mentioned this should be as simple for the user as opting-in. Your app users should be able to request that their entire data history is deleted and removed from all records. This includes third parties (yes that means every SDK that you have used in your app that uses personal data).

For developers, this means designing user control into the app so that the user can perform these actions when desired. Apps must be able to process and act upon these user requests and then ensure that all personal data is removed.

This might be in the form of an option to contact you with questions about your data.

Or you can add a data section to your app settings page that allows your users to opt out of different types of data collection. You can also add the option to revoke all data collection.

The aim of GDPR in this area is the put the user in control of their data. If you can design your app to facilitate this control then your app will be compliant and your users will have a better experience when using your app.


Privacy by design

This section is all about the proper encryption and data handling procedures.

You might think that this is an obvious approach to take when designing a mobile app. Perhaps you have considered privacy at multiple points in the planning of your app. That’s great – the key points to remember is that GDPR makes this a legal requirement.

So from a project’s inception to every point in the lifecycle privacy and data protection will need to be front and centre. It’s about anticipating, managing and preventing privacy issues. And doing this before a single line of code has been written.

There are fundamentals that app developers will do well to follow once the legislation comes into force:

Privacy must be proactive, not reactive, it must also be preventative not remedial. This means that developers should be thinking about privacy from stage one of the design process all the way through to after the user’s app engagement has ended.

Define the kinds of data that your app will use in the design phase. Assess potential issues that may arise when using this data. Make sure that your app is designed to secure this data by default and has the correct opt-in processes before you do anything with this data.

When processing user data ensure that your systems are designed to secure the data. This might mean pseudonymization of data or even creating a completely secure way of processing personal data.

The basic idea here is that privacy and data control to become a key part of designing any new app feature. By taking this approach you create an app experience that is secure. It provides users with the controls to input personal information in the knowledge that it is secured and that they can have it removed at any time.


Consent module and Tamoco’s secure SDK

As mentioned one area where developers need to ensure compliance with GDPR is through the use of third-party SDKs. Many of this access and use user data, and often there is not explicit consent for this from the end user.

If you’ve been paying attention you’ll realise that this is a direct breach of GDPR. As a developer, you’ll need to balance the use of third-party SDKs with user privacy and consent. Partnering with SDKs that place user opt-in front and centre will be a sensible approach once GDPR comes into effect.

At Tamoco we help apps to comply with the new regulation whilst providing a powerful toolkit to boost app engagement and monetization. Our product allows apps to get valuable insights and analytics into their app audiences whilst ensuring GDPR compliance.

[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”50px” bottom_margin=”20px”]

Manage consent today – sign up below to get free early access

[mkdf_button size=”” type=”” text=”Get early access” custom_class=”” icon_pack=”font_awesome” fa_icon=”” link=”contact-app/” target=”_self” color=”” hover_color=”” background_color=”” hover_background_color=”” border_color=”” hover_border_color=”” font_size=”” font_weight=”” margin=””]
 
[mkdf_separator class_name=”” type=”normal” position=”center” color=”#E8E8E8″ border_style=”solid” width=”100%” thickness=”3px” top_margin=”20px” bottom_margin=”0px”]

Related: read more about how Tamoco sources consented location data.

Categories
Privacy & Consent

Cleaning Up The Digital Supply Chain: GDPR Is Just The Start

It was Unilever’s Keith Weed that pulled no punches toward the digital media industry as a whole this week. His message was clear: “Clean up or get out.” It was made abundantly evident that Unilever was no longer ready to use its $8.5bn marketing budget to prop up the industry. Especially as it has been worryingly dismissive about their level of accountability on everything from data protection to trolling. 

Calling out the obvious culprits in GAFA, the broad-reaching topics that were referenced should have sent a direct message to the industry as a whole – to have more of a moral conscious and get its act together. But what’s the big deal all of a sudden? 

Well, for starters, this isn’t the first time that the issue of digital platforms misusing their power, reach and influence has been brought up. Nor is it the first time that a large media spender has threatened to pull their budgets if these aforementioned platforms didn’t get their act together. It is the first time that we’ve had a consecutive series of events in recent months. That gives Unilever and the wider media community a chance to bandwagon and create more of a stand against this ongoing farce. 


A drive for transparency

Keith’s message also did something quite novel. It gave some clear guidelines on what Unilever wanted to see in order to give it the comfort that appropriate steps had been taken to make progress in this area. Namely:

1.     Responsible platforms: Unilever will not do business with a platform that does not protect children, or which create division in society and promote anger or hate.

2.     Responsible content: Unilever is doubling down on its commitment to responsible content, initially by tackling gender stereotypes in advertising through the Unstereotype Alliance; 

3.     Responsible infrastructure: Unilever will only work with organisations that are committed to creating better digital infrastructure, such as aligning around one measurement system and improving the customer experience. 

One of the best things to come into the industry is this collective drive for transparency, which lies at the heart of the problems this sector is facing. It’s convoluted, unnavigable and untrustworthy. It’s losing credibility at an alarming rate and until now it has been sufficient to ‘talk the talk’ and not need to walk the walk. The status quo has been enough to demonstrate you’re doing something about it without actually doing something about it. Well, 2018 certainly feels like the year this will finally change. 


Cleaning up the digital supply chain

As a company that works in the world of location data, serving the digital platform industry including partners such as Unilever, we’ve seen how important transparency, relevancy and security are to every single part of the chain. We’ve placed these issues at the heart of what we do at Tamoco. We ensure that consent is properly attained. The data we collect is legitimate and accurately attributed as precisely as is possible. In doing this we hope to bring back some integrity and structure to the industry. 

Keith was right – consumers do not care about third party verification. The tools that advertisers such as Unilever use for personalisation, contextualisation and measurement aren’t important if the data underpinning them has not been obtained properly, and utilised in a regulated and transparent way. 

This is why GDPR is coming. Not to scaremonger the public or to shut down companies trying to use data and technology to improve services. GDPR exists to stamp out the types of unscrupulous digital platforms that misuse, mislead and misrepresent. It’s these platforms that make life harder for the industry as a whole. By promoting transparency, relevancy and security we hope to claw back some of the trust lost by the industry.  At Tamoco we are excited for 2018 to become the year of transparency and control. 

Related: read more about how Tamoco sources consented location data.